// product · available now
Kubernetes Hardening Kit
tested Kyverno policies, NetworkPolicies & Helm
Enforceable Kubernetes guardrails, not a PDF: Pod Security, default-deny NetworkPolicies, 21 tested Kyverno policies, Helm chart and audit CLI.
● instant download · secure checkout by Gumroad
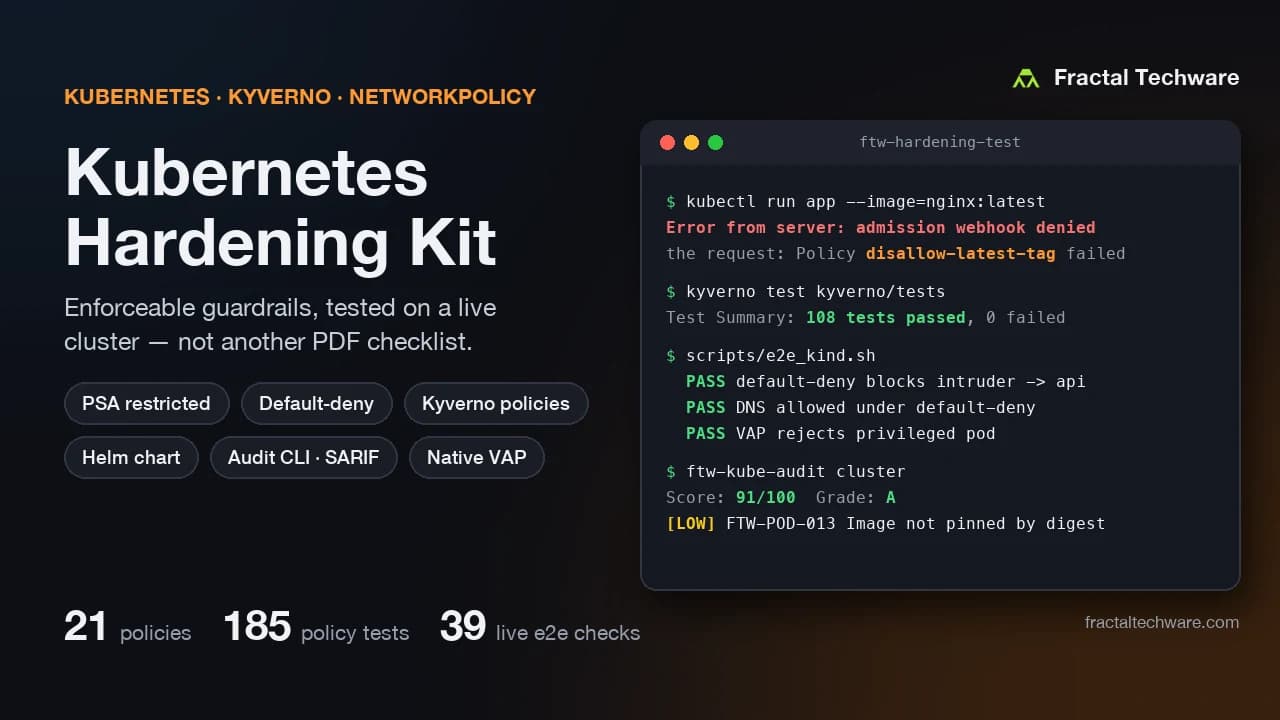
// tested
Tested, not just written
Every release runs its full test suite against real tooling before it ships.
Every Kyverno policy has passing and failing test resources (108 assertions)
Live kind cluster with Calico + Kyverno 1.19: privileged, root and :latest pods rejected
Default-deny proven: pod-to-pod traffic blocked while DNS and allowed paths work
722 resources validated with kubeconform -strict for Kubernetes 1.35 and 1.37
Native admission policies tested offline (77 assertions) and on the live cluster
Audit CLI covered by golden-file tests; builds offline to one static binary
// pricing
One-time purchase, three tiers
Pay once, keep the files. Each tier includes everything in the tier before it.
Starter
Small teams hardening their first cluster
$19USD
- Pod Security Admission restricted namespace
- Default-deny NetworkPolicy with DNS allowed
- Hardened Deployment / Pod templates
- Checklist mapped to CIS & NSA/CISA sections
- 30 days of updates
Pro
Platform engineers enforcing guardrails
$49USD
- 21 tested Kyverno policies with audit → warn → enforce overlays
- PolicyException workflow with owner, ticket and expiry
- ftw-baseline Helm chart: namespaces, PSA, NetworkPolicies, RBAC, policies
- 6 NetworkPolicy patterns, least-privilege RBAC, migration guide
- 1 year of updates
Studio
Consultants, agencies, security-minded teams
$99USD
- ftw-kube-audit CLI (Go): scored report, JSON and SARIF
- 15 native ValidatingAdmissionPolicies (no Kyverno needed)
- GitHub Actions workflow with SHA-pinned actions
- Rollout runbook, client-use license
- 1 year of updates
// contents
What's inside
- PSA restricted namespaceStarter+
- Default-deny NetworkPolicy + DNSStarter+
- Hardened workload templatesStarter+
- CIS / NSA-CISA mapped checklistStarter+
- 21 Kyverno policies + testsPro+
- PolicyException workflowPro+
- ftw-baseline Helm chartPro+
- 6 NetworkPolicy patternsPro+
- Least-privilege RBAC templatesPro+
- ftw-kube-audit CLI (SARIF)Studio+
- 15 ValidatingAdmissionPoliciesStudio+
- GitHub Actions gate + rollout runbookStudio+
// compatibility
Works with your stack
- Kubernetes 1.32 – 1.37 (tested live on 1.35 and 1.37)
- EKS, GKE, AKS, DOKS, OKE, k3s, kind
- Calico, Cilium, Antrea, AWS VPC CNI, GKE Dataplane V2
- Kyverno 1.19+ (Pro) or no policy engine (Studio VAP)
- Helm 3.14+ / 4 · GitHub Actions
// faq
Questions
+Will this break my cluster?
Not by default. Policies install in audit mode and only report; admission controls never evict running pods. The migration guide moves one namespace and one policy at a time, with a rollback for every step.
+Do I need Kyverno?
Starter needs only kubectl. Pro's policy library uses Kyverno 1.19+. Studio adds native ValidatingAdmissionPolicies that run in the API server with no extra components.
+My CNI is Flannel. Does default-deny work?
Flannel alone does not enforce NetworkPolicy. The compatibility matrix lists CNIs that do and shows how to prove enforcement in two minutes.
+Can I use it for client work?
Starter and Pro are licensed for your own organization. Client and agency use requires Studio.
+Refunds?
If the kit doesn't work with a supported setup and the troubleshooting guide doesn't fix it, contact us within 14 days for a refund.
Harden your cluster this week, not this quarter.
Questions first? Email hello@fractaltechware.com